Nothing Is Ever Really Gone: The Persistent Digital Residue That Survives Your Delete Key
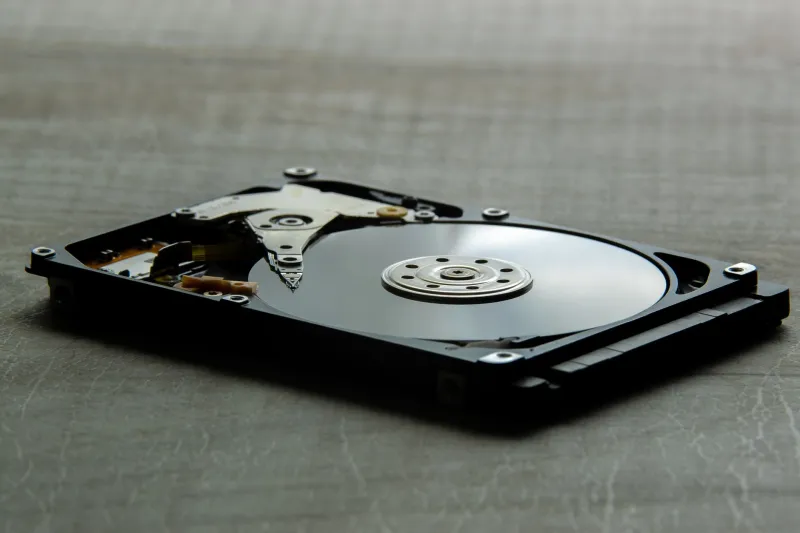
When federal investigators executed a search warrant on the home office of Paul Hansmeier — one of the attorneys behind the Prenda Law copyright trolling scheme — they recovered emails, documents, and financial records that Hansmeier believed he had permanently deleted. The digital forensics analyst assigned to the case did not require any extraordinary capability to retrieve them. Standard recovery tools, applied to a standard hard drive, surfaced the evidence that eventually contributed to Hansmeier's conviction on fraud and money laundering charges.
The Hansmeier case is not exceptional. It is illustrative. In courtrooms across the United States, digital forensic evidence recovered from devices whose owners believed them to be clean has become a routine feature of criminal prosecution, civil litigation, and regulatory enforcement. The gap between what users think deletion accomplishes and what it actually accomplishes is, in many cases, the gap between privacy and exposure.
What "Delete" Actually Means
To understand why deleted data persists, it helps to understand what the delete operation actually does on most consumer operating systems.
When you drag a file to the trash on a Windows or macOS machine and empty the trash, the operating system does not overwrite the data stored on the disk. It removes the file system entry — the index record that tells the operating system where the file lives and what it is called. The underlying data remains physically present on the storage medium until the operating system needs that space for something new and overwrites it with fresh data. On a lightly used drive with substantial free space, that overwrite may never occur during the practical lifespan of the device.
This is why tools like Recuva, PhotoRec, and the commercial forensic suite EnCase can recover files that were "deleted" months or even years earlier. They do not break encryption or defeat security controls. They simply read the raw storage medium and reconstruct files from data the operating system no longer indexes but has not yet erased.
Solid-state drives (SSDs) behave somewhat differently due to a process called TRIM, which more aggressively reclaims deleted storage blocks. However, the timing and completeness of TRIM operations vary by manufacturer and configuration, and forensic recovery from SSDs — while more variable than from traditional hard drives — remains achievable under many conditions.
The Shadow Beneath the Surface: Volume Shadow Copies and System Restore
Beyond simple file deletion, Windows systems maintain a feature called Volume Shadow Copy Service (VSS), which automatically creates point-in-time snapshots of the file system for backup and recovery purposes. These shadow copies can preserve versions of files that were subsequently modified or deleted — meaning that a document you edited and then erased may exist in its earlier form within a shadow copy you did not know existed.
Forensic investigators routinely examine shadow copies during evidence collection. In ransomware incidents, threat actors have begun targeting and destroying shadow copies specifically because they represent a recovery pathway — a tacit acknowledgment by criminal actors of how valuable these artifacts are.
macOS maintains a similar mechanism through Time Machine backups and, on Apple Silicon devices, system snapshots created during software updates. iOS and Android devices create encrypted backups to iCloud and Google One respectively, and these backups may contain data from apps and files that the user has since removed from the device.
EXIF Data and the Metadata Layer
File content is only one dimension of recoverable information. Metadata — data about data — constitutes an equally significant forensic resource, and it is one that most users never consider.
JPEG images captured by smartphone cameras embed a substantial quantity of metadata in the EXIF (Exchangeable Image File Format) header. This header typically records the camera make and model, the date and time of capture, exposure settings, and — critically — GPS coordinates if location services were active at the time of capture. A photograph shared online, even after the visible content has been cropped or edited, may retain its original EXIF data unless it has been explicitly stripped.
In 2012, John McAfee — the antivirus pioneer who was at the time evading Belizean authorities following a neighbor's murder — was located by journalists in part because photographs published alongside an interview retained GPS metadata placing him in Guatemala. The journalists had not intended to compromise his location. The camera had recorded it automatically.
Beyond images, Microsoft Office documents embed author names, organizational affiliations, revision histories, and in some versions, the file path of the original document on the author's machine. PDF files can contain similar metadata. These artifacts have surfaced in whistleblower identification cases, intellectual property disputes, and criminal investigations.
Browser Cache and the Artifacts of Navigation
Web browsers maintain local caches of visited pages, images, scripts, and cookies to improve loading performance. This cache constitutes a detailed record of browsing behavior that persists independently of the browser's history function. Clearing your browser history does not clear the cache. Clearing the cache does not clear cookies. Clearing cookies does not remove saved form data or autofill records. Each layer requires separate action.
Furthermore, browser forensic tools used by investigators can often reconstruct browsing sessions from cache artifacts even after a user has cleared history, deleted the cache, and uninstalled the browser — provided the underlying storage has not been overwritten.
Private or "incognito" browsing modes prevent local history from being written in a persistent form but do not prevent cache artifacts from being written to disk during the session. Research published by security academics has repeatedly demonstrated that incognito mode provides substantially less privacy protection at the device level than most users assume.
Secure Deletion: What It Actually Requires
Genuine data sanitization — the kind that defeats forensic recovery — requires deliberate action beyond what consumer operating systems provide by default.
On traditional hard drives, software tools that perform multiple-pass overwriting — such as Eraser for Windows or the srm command on macOS and Linux — replace deleted file data with random patterns, making reconstruction substantially more difficult. The US Department of Defense historically specified a seven-pass overwrite standard (DoD 5220.22-M); for most civilian purposes, a single-pass overwrite of free space is considered adequate.
On solid-state drives, overwriting is less reliable due to wear-leveling algorithms that distribute writes across the drive in ways that may leave some blocks unwritten. The most dependable sanitization method for SSDs is full-disk encryption prior to use, combined with secure erasure of the encryption key — a method that renders remaining data cryptographically inaccessible even if physically recovered.
For cloud storage, deletion is complicated by replication and backup infrastructure. Files deleted from Google Drive, iCloud, Dropbox, or OneDrive may persist in version history, deleted file retention bins (typically 30 days), and backend backup systems for periods determined by each provider's internal policies. Review each platform's data retention documentation and explicitly purge deleted file bins after removal.
For smartphones, a factory reset preceded by full-device encryption is the recommended sanitization approach before disposal or resale. On modern iPhones running iOS 15 or later, a factory reset on an encrypted device is considered sufficient for most threat models.
The Forensic Reality and Its Implications
The persistence of digital data is not inherently sinister. The same capabilities that allow investigators to recover evidence against fraudsters and criminals also allow journalists to verify documents, allow victims to recover accidentally deleted photographs, and allow organizations to restore operations after ransomware attacks.
What is problematic is the widespread public misunderstanding of what deletion means and what privacy controls actually protect. For ordinary users concerned about sensitive personal data — medical records, financial documents, private correspondence — the practical implication is straightforward: if you want data to be gone, you must take deliberate steps to make it gone. The delete key, by itself, is not among those steps.